Auth · SSO · 2025
HanDev Identity
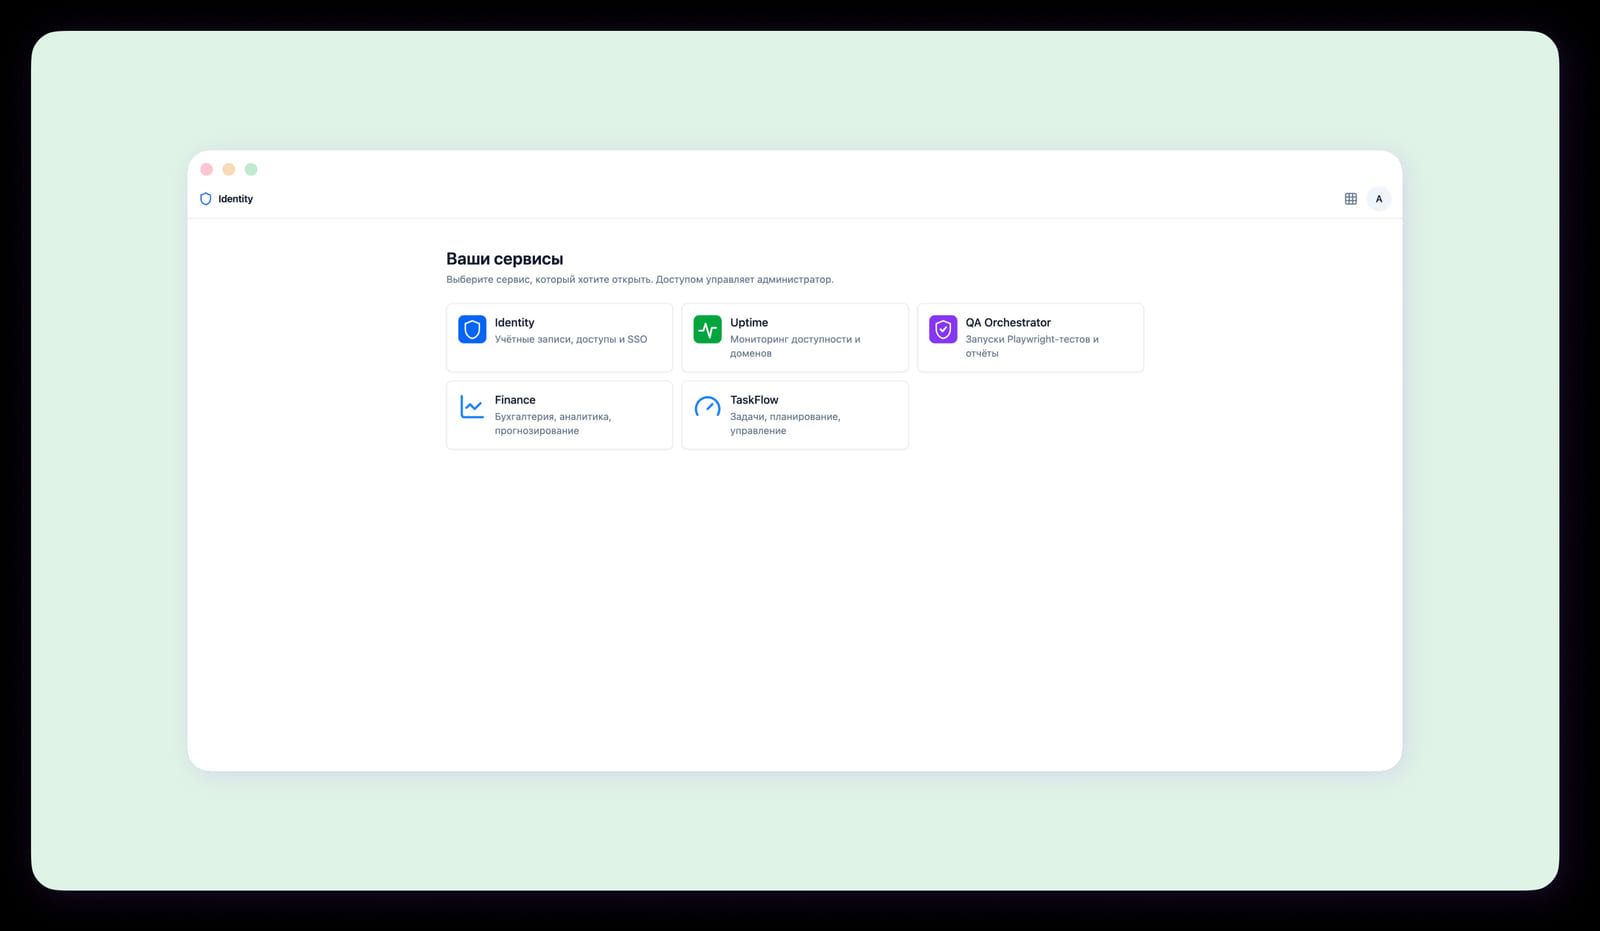
Central SSO service (auth.handev.org): issues JWTs, publishes JWKS, manages users, services and access rights.
- RS256 JWT + JWKS endpoint
- Triple refresh: 401 retry / 12-min tick / visibilitychange
- User × service access matrix
- GitLab OAuth for corporate accounts
Node 22FastifyDrizzlePostgreSQLReact 18
Challenge
The platform needed a central auth hub: single sign-on across all services, key rotation, correct token refresh from background tabs, per-service access gating, and an admin panel for users and access rights.
What We Did
- Backend on Fastify + Drizzle with custom token verification (no jsonwebtoken dependency), bcrypt for passwords.
- JWT claim shape: iss, sub, exp, iat, email, name, isAdmin, globalRole, services. RS256 signatures, keys rotated, JWKS at /.well-known/jwks.json.
- 15-min access + 30-day refresh, both as HttpOnly cookies on .handev.org with SameSite=lax.
- Triple refresh: /auth/refresh retry on 401, 12-min tick, refresh on visibilitychange.
- Admin pages: /admin/users, /admin/services, /admin/access (user × service matrix).
- Service-access gate: grant in user_service_access + payload.services check in each service.
- GitLab OAuth for linking corporate GitLab accounts to Identity users.
Result
- Single login for 3 services; adding a new service requires just a couple of SQL inserts and build-deploy.
- Production-ready SSO with proper refresh and 401 recovery.
- Clear separation of global role and service-internal role.
Let's
talk.
We reply within one business day with an initial assessment and the nearest team slot.
✉ info@handev.org